Risks and opportunities (ISO 9001 clause 6.1): a practical approach without the bureaucracy
TürkçeEnglish
Practical advice for identifying risks and opportunities from context and interested parties, a simple assessment method, action plans and monitoring.
Risk-based thinking is one of the most misunderstood topics in ISO 9001. Some companies build risk registers with hundreds of lines, others settle for a generic one-page list. The aim is to see in time the issues that could really affect your business, and manage them.
Start from context
Risks do not come out of nowhere. First write down internal and external issues (4.1) and the expectations of interested parties (4.2): dependence on a key customer, raw material prices, experienced staff retiring, new legislation. This list is the natural source of risks and opportunities.
Choose a simple method
A 3×3 likelihood-impact matrix is enough for most companies. What matters is applying it consistently and deciding in advance which score requires action. Complex formulas do not add reliability; they add debate.
Do not forget opportunities
Clause 6.1 covers opportunities as well as risks: a new customer segment, software that reduces scrap, an investment that improves efficiency. Opportunities can also be assessed and linked to an action plan.
Action plan and monitoring
Define an action with an owner and a date for every high-scoring risk. Reassessing the risk after the action shows whether it worked. Review risks at least once a year and after significant changes.
- Risk: single-source supplier → Action: approve a second supplier
- Risk: critical machine breakdown → Action: spare parts stock and service contract
- Opportunity: cutting optimisation → Action: trial and measure scrap rate
Risks and opportunities in QMOS
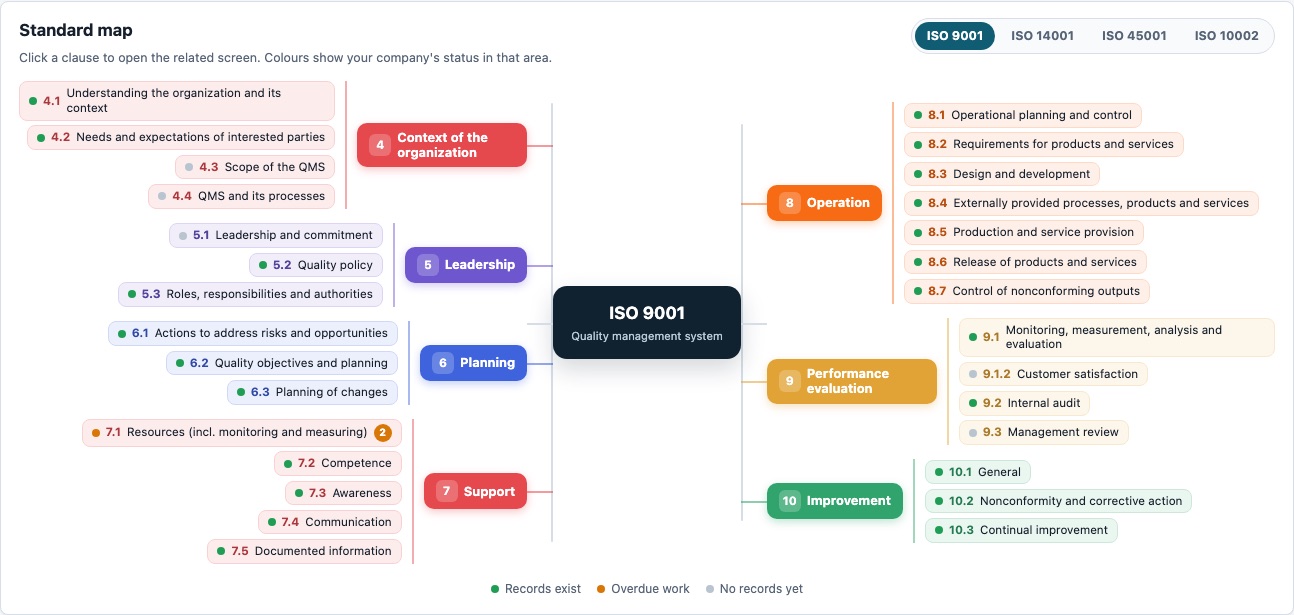
In QMOS context and interested parties, risks and opportunities and quality objectives are linked screens. The assessment method is defined per company and versioned; critical risks without an action plan are flagged and actions become tasks for their owners.
Sık sorulan sorular
Is FMEA required for risk analysis?
No. The standard does not require a specific method; a consistent method that suits your size and complexity is enough.
How often should the risk register be updated?
At least once a year and whenever processes, customers or legislation change significantly.